
Compliance & Frameworks
ISO 42001, NIST AI RMF, EU AI Act, SEC/FINRA — how to map and prove controls.
Verifiable Evidence Lineage: A Buyer's Guide
How to judge whether a governance platform can prove its own evidence — chained hashing, daily seals, file fingerprinting, and signed audit packs.
7 min read
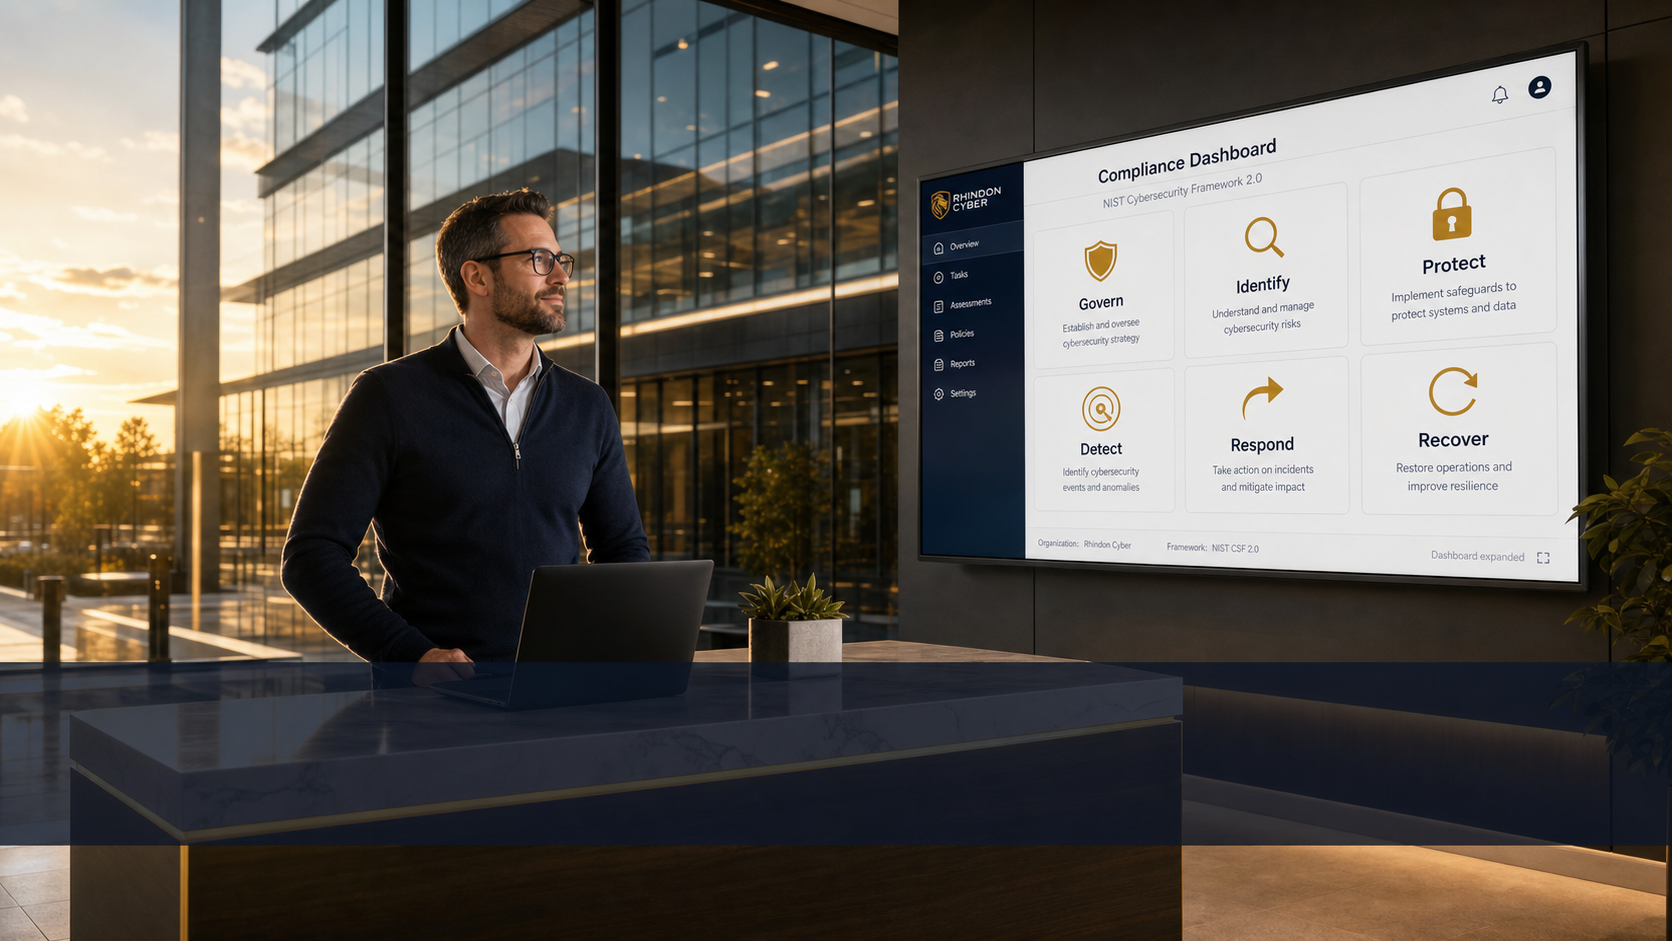
NIST CSF 2.0 for Small and Medium Businesses: A Practical Compliance Guide
Where NIST CSF 2.0 provides the internal risk management architecture, SOC 2 provides the external attestation that enterprise buyers and regulators use to assess a vendor's security posture. The two frameworks are not redundant — they are mutually reinforcing. NIST CSF 2.0's six functions map directly to SOC 2's Common Criteria (CC) series
11 min read
SOC 2 and AI Governance in 2026: The Complete Guide for SMBs
Shadow AI — the use of AI-powered tools by employees without IT approval or governance controls — has emerged as one of the most common SOC 2 audit findings in 2026.
15 min read
ISO 42001: The Complete Guide for SMBs — What It Is, Why It Matters, and How to Get Certified (2026)
22 min read