
THE AI YOU DIDN'T SANCTION
IS ALREADY IN PRODUCTION.
Shadow AI is the unsanctioned use of AI tools inside your business — the chatbots, copilots, and AI add-ins your employees adopted without IT review. RAIC continuously detects supported AI services and model activity from browser and Microsoft 365 signals, matched against its curated AI catalog, then scores the risk and routes the dangerous ones into governance automatically.
The AI your team uses that nobody approved.
Shadow AI is the AI equivalent of Shadow IT — but faster, broader, and harder to detect. A marketer pastes a quarter's worth of CRM data into a chatbot to draft an email. An engineer pipes proprietary code into a model trained on the open web. A finance analyst uploads board materials to summarize them. None of it goes through procurement. None of it gets a vendor review. None of it appears in your AI inventory.
By the time you find out, the data is gone, the audit is open, and you're explaining to the board why your AI governance program doesn't include the AI your company actually uses.
Shadow AI is the #1 AI governance risk of 2026 — and the one most organizations are still trying to address with a spreadsheet survey.
What you can't see is already costing you.
Data leakage you'll find out about last
Employees paste customer PII, source code, and contracts into free chatbots. Once it's in someone else's model, you can't claw it back.
Compliance gaps you can't map
ISO 42001, NIST AI RMF, and the EU AI Act all require an inventory of AI systems in use. You can't govern what you can't see.
Audit findings written in your name
Auditors are now opening with "show me your AI inventory." A blank stare or a stale spreadsheet is a finding waiting to be written.
Vendor risk you never assessed
Every unsanctioned AI tool is an unvetted vendor — with its own data retention, training policy, and security posture you've never reviewed.
Two signals. Continuous coverage.
Stop asking employees to self-report. Detect Shadow AI where it actually lives — in the browser and in your Microsoft 365 tenant. RAIC matches against a curated detection catalog of AI web apps, models, and AI API endpoints, continuously expanded by an automated curation pipeline with confidence-gated auto-promotion of new signals.
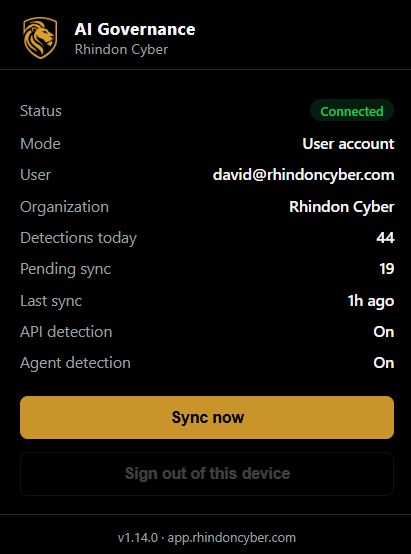
Chrome and Firefox extension (v1.18.3)
A lightweight extension for Chrome and Firefox records supported AI web apps your team uses — ChatGPT, Claude, Gemini, Perplexity, and the long tail of niche tools in RAIC's curated catalog — with no keystroke logging and no content capture.
Model-level detection across thousands of AI services
Detection runs against a continuously curated catalog covering thousands of AI services and their models, so you see not just which tool was used but which model was called — and new tools land in your inventory as they appear.
Microsoft Graph NHI ingest
Pull non-human identities, service principals, AI add-ins, Copilot usage, and OAuth-consented AI apps straight from Microsoft Graph. See exactly which AI tools and bots hold access to your corporate data.
AI agent and automation session scoring
Three signal families — DOM, timing, and entropy — score whether a session was driven by a human or an AI agent, banded Suspected, Likely, or Confirmed so your team triages the strong signals first.
Auto-route risky tools into intake
When a high-risk AI tool shows up, RAIC opens an intake workflow automatically — risk scoring, policy attestation, and supervisor sign-off without you chasing anyone down.
Privacy by design: the extension reads the URL path and the JSON model field of outbound AI calls only. It never captures page content, prompts, responses, or keystrokes.
Deploy. Discover. Triage. Govern.
Deploy
Push the browser extension via Intune or your MDM. Connect Microsoft 365 with a delegated admin consent. Live in under an hour.
Discover
RAIC records supported AI services and model activity across the organization — sanctioned, unsanctioned, and everything in between — matched against its curated catalog.
Triage
Each discovered tool is risk-scored against your policy. High-risk tools are flagged. Low-risk tools are noted and tracked.
Govern
Promote sanctioned tools into the AI registry. Block or restrict the rest. Export the full inventory for your next audit.
Real visibility. Real governance.
- Build a real inventory of the AI your employees use — in days, not quarters
- Catch a customer-data leak before it lands in your CISO's inbox
- Hand the auditor a real AI inventory, not a spreadsheet from last year
- Cut Shadow AI risk without banning AI outright
- Promote the tools that actually help; block the ones that don't
- Turn discovery into a board-ready posture metric
From the Resources library
Dig deeper into Shadow AI detection methodology, research, and field playbooks.
STOP GUESSING. START SEEING.
Spin up RAIC in your tenant and see Shadow AI in your environment within a day.
Self-service online demo — explore RAIC's modules and workflows on your own time, no scheduling required.
MSP, reseller, and audit-partner programs. Email the partner desk.