
RUN AI COMPLIANCE
WITHOUT DROWNING IN SPREADSHEETS.
RAIC gives compliance, GRC, and risk teams one platform to govern every AI system, attest every control, and export audit-ready evidence on demand — mapped to ISO 42001, NIST AI RMF, and the EU AI Act out of the box.
You're the team the regulator calls first.
And right now, you're answering with a spreadsheet that hasn't been reconciled since the last audit.
Shadow AI you can't see
Employees are pasting customer data into chatbots your policy never approved. You'll find out from an auditor or a breach — whichever comes first.
Evidence trapped in spreadsheets
Risk registers, control matrices, and attestation logs live in five different sheets. Every audit cycle becomes a two-week scramble to reconcile them.
Three frameworks. One team.
ISO 42001, NIST AI RMF, and the EU AI Act each demand their own evidence shape — and your headcount didn't triple to match.
Board questions you can't answer in 24 hours
"How many AI systems are we running? Which ones are high-risk? Who signed off?" If the answer takes a week, you've already lost the room.
An AI Management System your auditor recognizes on sight.
Stand up an AI Management System in days, not quarters
Pre-built intake workflows, control libraries, policy templates, and attestation flows — operational the day you sign up. No six-month consulting build.
One control mapped to every framework you care about
Write the control once; RAIC maps it to ISO 42001 Annex A, NIST AI RMF subcategories, and EU AI Act articles — and exports framework-specific evidence on demand.
Find Shadow AI before the auditor does
The browser extension and Microsoft Graph integration detect supported AI services and model activity, matched against RAIC's curated catalog — and route the high-risk ones into intake automatically.
Auditor-ready evidence at one click
Statement of Applicability, control evidence packs, attestation history, executive summaries — exported as branded DOCX, CSV, or ZIP, each pack signed so your auditor can verify it independently. Hand it over without reformatting.
Exceptions and waivers that expire on their own
Register every time-bounded departure from a control with an owner, a reason, and an expiry date — and see it surface before it lapses instead of after the finding.
A governance calendar and an escalation ladder
Reviews, attestations, meetings, and expiries sit on one calendar, and stalled decisions move up a defined path rather than waiting for someone to notice.
Aslan AI drafts the artifacts you used to write by hand
Risk assessments, gap analyses, policies, executive summaries, incident playbooks — drafted in minutes from your live registers, then reviewed and approved by you.
A live posture score for the board
Governance Dashboards give your CISO and audit committee a real-time view of what's governed, what's exposed, and where the evidence trail is thin.
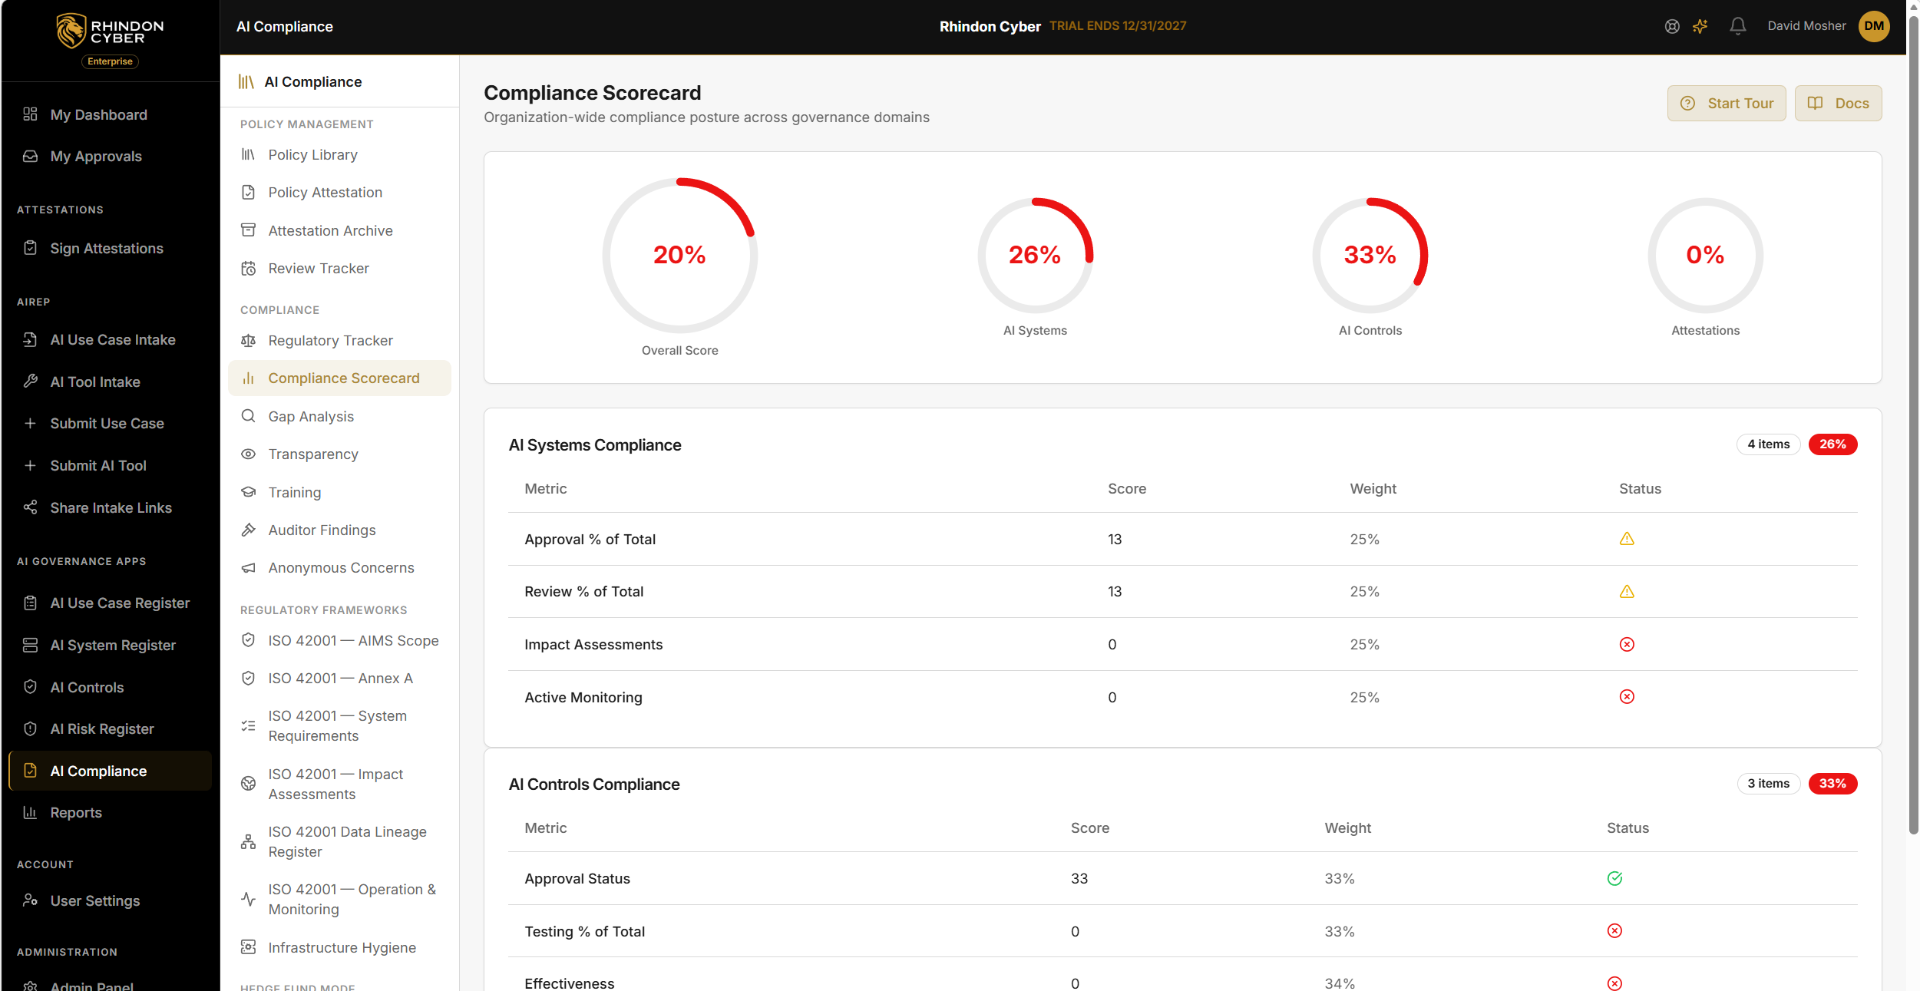
The Compliance Scorecard — live posture across AI Systems, Controls, and Attestations in one view.
Discover. Intake. Control. Prove.
Discover
Inventory every AI system and surface Shadow AI across the browser and Microsoft 365 — no manual census required.
Intake & Score
Route every new AI use case through a staged intake. Risk-score against EU AI Act, NIST, and ISO 42001 — automatically.
Control & Attest
Attach pre-mapped controls, draft policies, and collect attestations with versioning and approval history.
Prove
Export audit-ready evidence: SoA, control packs, exec summaries, and recertification ZIPs — branded and ready to hand off.
One platform. Every framework your auditor expects.
Write a control once. Export evidence in the shape each regulator demands.
ISO/IEC 42001
Full Annex A coverage with SoA export, internal audit cadence, nonconformity register, and management review packs.
Framework detailsNIST AI RMF
Govern, Map, Measure, Manage — RAIC's controls library is mapped to every subcategory with evidence linkage.
Framework detailsEU AI Act
Provider and Deployer actor scoping, risk classification, and Annex IV / XI / XII / XIII evidence packs.
Framework detailsSEC / FINRA AI
ADV Part 2A drafting, FINRA WSP register, and supervisor sign-offs for registered investment advisors.
Framework detailsThe work that used to eat your week.
- Cut audit-prep time from weeks to days
- Stop chasing department heads for control evidence
- Replace the AI use case spreadsheet with a real workflow
- Give the board a posture score on demand
- Catch a Shadow AI breach before it lands on your desk
- Draft a risk assessment in three minutes, not three hours
- Close out an exception before it becomes an audit finding
Who was allowed to decide? RAIC's Governance Operations & Decision Rights capability names the authority behind every approval, records every refusal, and exports the Governance State & Continuity Pack for your assessor.
The EU AI Act is enforceable. ISO 42001 is the bar.
Boards are asking the AI question. Auditors are writing the AI section into their fieldwork plans. The teams that wait until next quarter are the ones writing remediation plans next year. Start now and walk into the next audit with the evidence already exported.
From the Resources library
Framework-by-framework guidance for your next audit.