
NIST CSF 2.0 for Small and Medium Businesses: A Practical Compliance Guide
--
Table of Contents
- What Is NIST CSF 2.0 — and Why Does It Matter for SMBs?
- The Six Functions: What SMBs Must Do
- AI Cybersecurity and the Expanding Attack Surface
- NIST CSF 2.0 and SOC 2: How They Align
- Building a Practical CSF Program Without a CISO
- How RAIC Delivers NIST CSF 2.0 for SMBs
- References
What Is NIST CSF 2.0 — and Why Does It Matter for SMBs?
The NIST Cybersecurity Framework (CSF) 2.0 is a voluntary, risk-based set of standards, guidelines, and best practices published by the National Institute of Standards and Technology to help organizations manage and reduce cybersecurity risk (National Institute of Standards and Technology [NIST], 2024a). Originally developed in 2014 for critical infrastructure, Version 2.0 — released in February 2024 — explicitly expands the framework's applicability to organizations of all sizes and sectors, including small and medium businesses without dedicated security staff (NIST, 2024a).
What changed the business calculus for SMBs is not the framework itself — it is who anchors to it. Ross (2024), writing in the ISACA Journal, notes that the CSF has become a de facto international standard, of interest not only to U.S. organizations but to those in other countries as well. Cyber insurers now price premiums against demonstrable framework alignment, and enterprise procurement teams increasingly require evidence of a structured cybersecurity program before signing vendor agreements. Whitman and Mattord (2021) similarly observe that voluntary guidance has progressively functioned as a practical prerequisite for organizational accountability in an environment where regulators and buyers treat recognized frameworks as the baseline of prudent practice.
NIST published a dedicated Small Business Quick Start Guide alongside CSF 2.0, recognizing that SMBs with modest or no existing cybersecurity plans need a practical entry point rather than an enterprise-scale implementation manual (NIST, 2024b). The Dempsey et al. (2024) analysis in The CPA Journal reinforces this point, observing that CSF 2.0's flexibility and relatively concise structure make it especially well-suited to organizations that must adapt the framework to a limited resource environment while still satisfying financial management oversight responsibilities.
The Six Functions: What SMBs Must Do
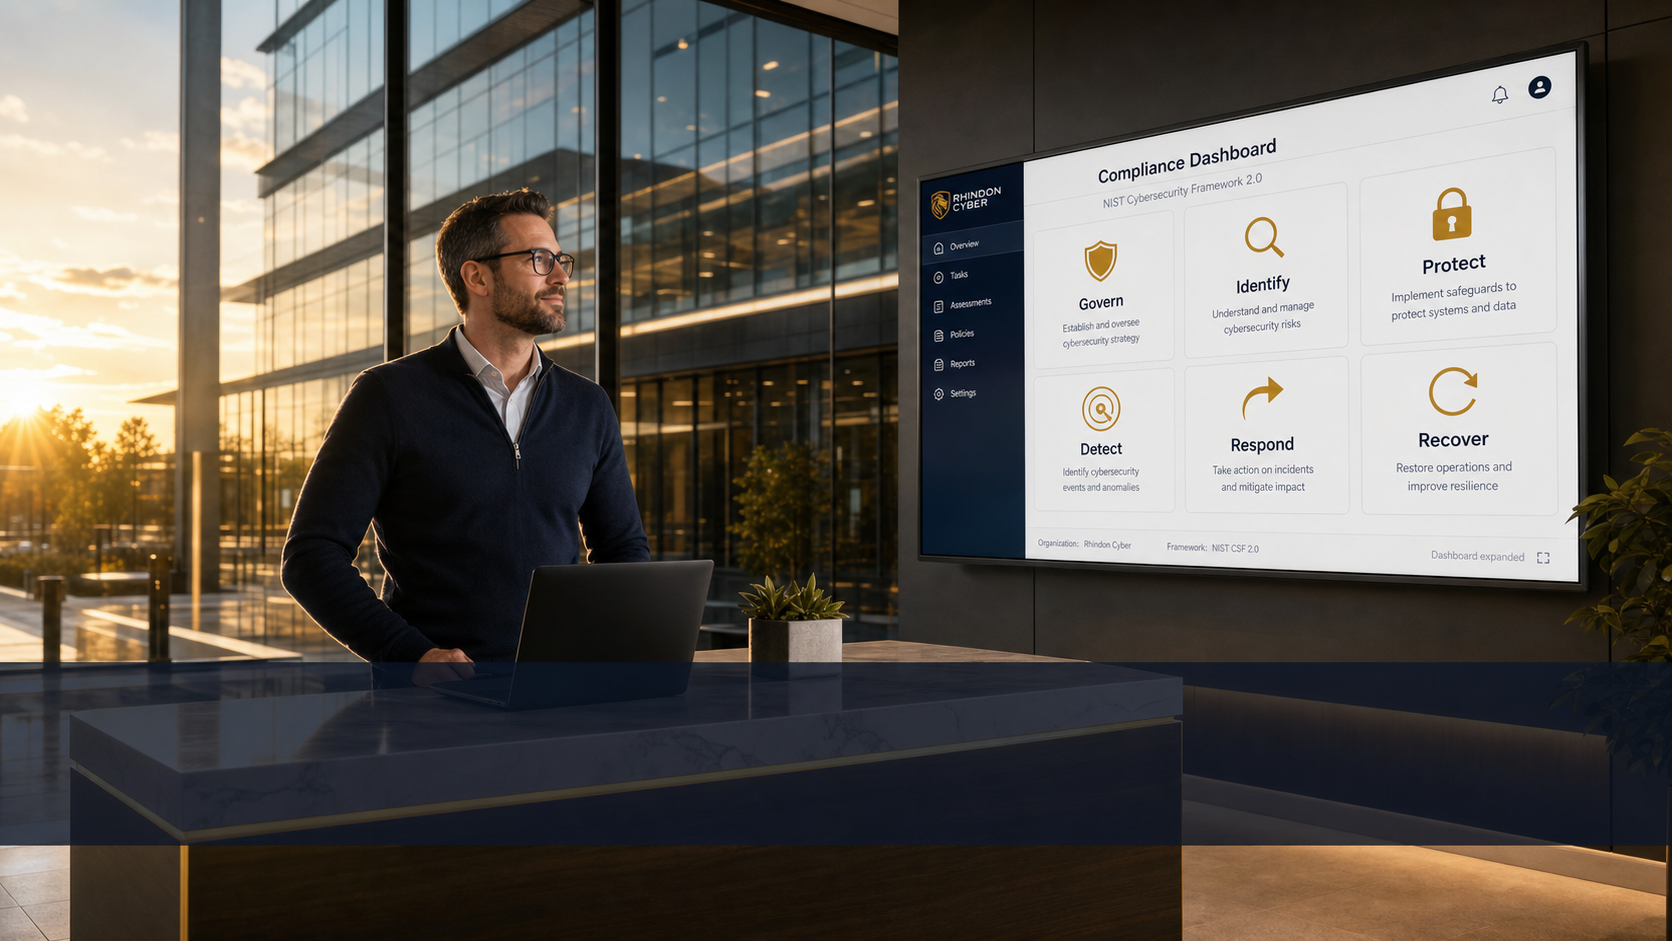
NIST CSF 2.0 organizes cybersecurity activities into six interconnected core functions (NIST, 2024a). Each function addresses a distinct phase of cybersecurity risk management, and all six must be addressed for a program to be considered complete.
Govern is the new function introduced in CSF 2.0. It establishes cybersecurity risk management strategy, expectations, policy, roles, and accountability at the leadership level. Ross (2024) highlights that CSF 2.0's explicit governance hierarchy — executives, managers, and practitioners — represents a significant departure from earlier versions and directly addresses the accountability gap that allowed cybersecurity to remain siloed below board level. For SMBs, this translates to a documented policy set, a named cybersecurity program owner, and a defined risk tolerance.
Identify requires organizations to develop a comprehensive understanding of their assets, suppliers, and cybersecurity risks. In practice, this means maintaining a current asset inventory — hardware, software, SaaS applications, and data categories — paired with a supply chain risk register that includes third-party vendors and any AI model providers in use (NIST, 2024a). Quainoo and Ahad (2026) note that for digital SMEs, the failure to maintain a complete asset inventory is among the most pervasive non-technical barriers to responsible AI and information security governance.
Protect covers the safeguards that reduce the likelihood of a cybersecurity event. Priority controls for most SMBs include multi-factor authentication, privileged access hardening, endpoint detection and response across all devices, and data classification with access controls on sensitive content (NIST, 2024a; Dempsey et al., 2024).
Detect addresses the timely discovery and analysis of cybersecurity events. SMBs should implement monitoring that surfaces anomalies, indicators of compromise, and — critically — unsanctioned technology use, including AI tools that employees adopt without IT approval (ISACA, 2025).
Respond defines how the organization acts when a cybersecurity event is detected. This requires an incident response plan aligned to detection outputs, with defined playbooks, communication trees, and evidence preservation procedures that satisfy both operational and audit requirements (NIST, 2024a).
Recover ensures that affected systems and services are restored following an incident. For SMBs, this means documented and tested backup and recovery procedures, with restoration success rates tracked as a key performance indicator. Dempsey et al. (2024) note that CSF 2.0's supply chain enhancements strengthen the Recover function by requiring organizations to account for third-party recovery dependencies — a gap often invisible in legacy plans.
AI Cybersecurity and the Expanding Attack Surface
AI is not just a tool SMBs can use for productivity — it is a risk factor that every NIST CSF 2.0 program must now address. NIST published a draft Cybersecurity Framework Profile for Artificial Intelligence (Cyber AI Profile) in December 2025, organized around three focus areas: securing AI system components, conducting AI-enabled cyber defense, and thwarting AI-enabled cyber attacks (NIST, 2025a). The Cyber AI Profile is explicitly designed as a supplement to CSF 2.0, not a replacement, and applies to organizations at any stage of AI adoption.
The AI risk facing SMBs is not primarily advanced adversarial attacks — it is shadow AI. ISACA (2025) defines shadow AI as the unauthorized use of AI solutions — including chatbots, code assistants, and large language models — to perform job tasks without approval from IT or compliance teams. Unlike authorized AI systems, which undergo testing and evaluation before adoption, shadow AI tools create governance silos that are often dangerous for enterprise risk management. The IBM Cost of a Data Breach Report 2025, as reported in FM Magazine (AICPA, 2025), found that security incidents involving shadow AI accounted for 20% of data breaches globally and were more expensive for organizations to resolve than other breach types.
Agentic AI workloads introduce a second risk category. Autonomous AI agents that access APIs, manage workflows, and interact with external services require the same identity governance, least-privilege access controls, and behavioral monitoring applied to human users (World Economic Forum, 2025). The World Economic Forum (2025) — drawing on research conducted jointly with the University of Oxford's Global Cyber Security Capacity Centre — recommends that leaders establish an authoritative AI and IT catalogue with clear ownership as the foundational governance action, directly mapping to the Identify and Govern functions of CSF 2.0.
Quainoo and Ahad (2026) further observe that organizational culture, employee awareness, and stakeholder engagement are critical yet underrepresented components of AI and information security governance in digital SMEs, despite their pivotal role in sustaining the people, processes, and technology balance that effective compliance requires. This finding underscores that NIST CSF 2.0 implementation in SMBs must address the human factor — not just technical controls — to be durable.
The NIST AI RMF (NIST, 2023) and ISO/IEC 42001 — the international standard for AI management systems — provide the specialized governance vocabulary for AI risk that CSF 2.0's subcategories reference but do not fully prescribe. ISACA (2025b) advises organizations building toward regulatory readiness to treat these frameworks as complementary governance layers: CSF 2.0 provides the cybersecurity architecture, the AI RMF structures AI-specific risk management, and ISO 42001 provides the management system scaffold for ongoing AI governance.
NIST CSF 2.0 and SOC 2: How They Align
SOC 2 — System and Organization Controls 2 — is an attestation framework developed by the American Institute of Certified Public Accountants (AICPA) that evaluates whether a service organization's controls protect the security, availability, processing integrity, confidentiality, and privacy of customer data (AICPA, 2017). Where NIST CSF 2.0 provides the internal risk management architecture, SOC 2 provides the external attestation that enterprise buyers and regulators use to assess a vendor's security posture.
The two frameworks are not redundant — they are mutually reinforcing. NIST CSF 2.0's six functions map directly to SOC 2's Common Criteria (CC) series: the Govern function aligns with CC1 (control environment) and CC2 (information and communication); Identify aligns with CC3 (risk assessment) and CC9 (vendor management); Protect aligns with CC6 (logical access); Detect aligns with CC7 (system monitoring); and Respond and Recover align with CC5 (control activities) and CC4 (ongoing monitoring) (IS Partners LLC, 2025). An SMB that builds a rigorous NIST CSF 2.0 program is simultaneously constructing the control infrastructure required for a SOC 2 Type I engagement.
In 2026, AI governance has become an explicit component of SOC 2 scope. The AICPA's updated trust services guidance expanded Common Criteria CC3, CC6, CC7, and CC9 to include AI systems, AI vendors, and shadow AI tools (Rhindon Cyber, 2026). SMBs that cannot document how they govern AI tools — including which vendors process customer data, how shadow AI is discovered and remediated, and how model behavior is monitored — will face qualification delays and reopened audit fieldwork. A NIST CSF 2.0 program with integrated AI governance is the most direct path to SOC 2 readiness.
Building a Practical CSF Program Without a CISO
The most common reason SMBs delay NIST CSF 2.0 implementation is the belief that it requires enterprise-level resources. It does not. NIST's own Small Business Cybersecurity: Non-Employer Firms guidance (NIST, 2025b) demonstrates that even very small firms can use CSF 2.0 to begin managing cybersecurity risk with limited staff and budget.
A practical implementation follows five recurring activities (NIST, 2024a; Dempsey et al., 2024):
- Conduct a current-profile assessment. Score each of the six functions against CSF Tiers 1–4, documenting where controls exist and where gaps create the greatest exposure. Most SMBs begin at Tier 1 (partial) and target Tier 2 (risk-informed) or Tier 3 (repeatable) within 12–18 months.
- Define a target profile. Based on the organization's risk tolerance, industry vertical, and customer contractual requirements, set a target tier for each function. This becomes the strategic anchor for all gap-closure decisions.
- Build a gap-closure roadmap with named owners. For each identified gap, document what closes it, who owns it, estimated cost, and timeline.
- Map existing security investments to CSF functions. Assign the tools and services already in place to specific functions and subcategories. This exercise surfaces duplication, reveals gaps, and produces documentation that justifies spend to insurers and auditors.
- Schedule an annual review and executive report. A documented annual review of the current profile, gap progress, and updated target profile transforms CSF from a one-time exercise into a continuous program — and produces the artifact that insurers, customers, and auditors request.
Quainoo and Ahad (2026) emphasize that governance in SMEs does not need to be heavy; what matters is that it integrates people, processes, and technology as a coherent system rather than treating them as separate workstreams. Organizations with limited internal staff should engage a managed provider to share the operational load while retaining internal oversight of risk decisions.
How RAIC Delivers NIST CSF 2.0 for SMBs
RAIC (AI Risk & Integrity Cloud) by Rhindon Cyber was built to solve the exact problem NIST CSF 2.0 creates for SMBs: assessment, evidence, remediation, and reporting should not require four separate tools, a full-time analyst, and a quarterly scramble before every audit.
RAIC provides full NIST CSF 2.0 coverage across all six functions and the complete subcategory catalog. A guided assessment produces a live gap heatmap — scored by current and target tier — within hours of onboarding. Every identified gap converts automatically into a tracked remediation item in the integrated Plan of Action and Milestones (POA&M) register, with tamper-evident evidence attached directly to the relevant subcategory (Rhindon Cyber, 2026).
For SMBs pursuing SOC 2 or managing AI risk, RAIC's cross-framework crosswalk capability maps NIST CSF 2.0 subcategories live to ISO 42001, NIST AI RMF, EU AI Act, and SOC 2 — so a single gap-closure effort satisfies multiple frameworks simultaneously. AI systems, including shadow AI tools discovered through RAIC's detection capability, roll up into CSF subcategories so AI risk appears in the same posture report as the rest of the program. Board-ready snapshots capture point-in-time posture for trend reporting and drop directly into cyber insurance renewal questionnaires.
For organizations ready to move from assessment to attestation, RAIC bridges the gap between a NIST CSF 2.0 current profile and a SOC 2-ready control environment — without requiring a second GRC platform, a second vendor contract, or a second evidence workflow.
Start a free trial of RAIC or book a live demo at app.rhindoncyber.com/trial-signup. Assess your NIST CSF 2.0 posture across all six functions and see your AI risk in a single pane of glass.
References
American Institute of Certified Public Accountants. (2017). Trust services criteria for security, availability, processing integrity, confidentiality, and privacy (with revised points of focus — 2022). AICPA.
AICPA. (2025, August 14). Shadow AI emerges as significant cybersecurity threat. FM Magazine. fm-magazine.com/news/2025/aug/shadow-ai-emerges-as-significant-cybersecurity-threat
Dempsey, K., Eavey, P., & Goren, N. (2024, September). The updated NIST cybersecurity framework. The CPA Journal, 94(9). cpajournal.com/2024/09/17/the-updated-nist-cybersecurity-framework
IS Partners LLC. (2025, August 17). NIST vs SOC 2: Which compliance program suits your organization? IS Partners LLC. ispartnersllc.com/blog/nist-vs-soc-2
ISACA. (2025a, September 25). The rise of shadow AI: Auditing unauthorized AI tools in the enterprise. ISACA Industry News. isaca.org/resources/news-and-trends/industry-news/2025/the-rise-of-shadow-ai-auditing-unauthorized-ai-tools-in-the-enterprise
ISACA. (2025b, January). Leveraging COBIT for effective AI system governance [White paper]. ISACA. isaca.org/resources/white-papers/2025/leveraging-cobit-for-effective-ai-system-governance
National Institute of Standards and Technology. (2023, January). AI risk management framework (AI RMF 1.0) (NIST AI 100-1). U.S. Department of Commerce. nist.gov/itl/ai-risk-management-framework
National Institute of Standards and Technology. (2024a, February 26). The NIST cybersecurity framework (CSF) 2.0 (NIST CSWP 29). U.S. Department of Commerce. nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.29.pdf
National Institute of Standards and Technology. (2024b, February 25). NIST cybersecurity framework 2.0: Small business quick start guide (SP 1300). U.S. Department of Commerce. csrc.nist.rip/pubs/sp/1300/final
National Institute of Standards and Technology. (2025a, December 15). Cybersecurity framework profile for artificial intelligence (NIST IR 8596, initial public draft). U.S. Department of Commerce. nvlpubs.nist.gov/nistpubs/ir/2025/NIST.IR.8596.iprd.pdf
National Institute of Standards and Technology. (2025b, April 30). Small business cybersecurity: Non-employer firms (NIST IR 7621r2, initial public draft). U.S. Department of Commerce. nvlpubs.nist.gov/nistpubs/ir/2025/NIST.IR.7621r2.ipd.pdf
Quainoo, C. R., & Ahad, M. A. R. (2026). The role of information security in responsible AI for digital SMEs: A systematic review of frameworks, challenges, and best practices. Journal of Ethics and Emerging Technologies, 36(1), 1–29. doi.org/10.55613/jeet.v36i1.193
Rhindon Cyber. (2026, June 11). SOC 2 and AI governance in 2026: The complete guide for SMBs. Rhindon Cyber. raic.rhindoncyber.com/resources/compliance/ai-governance-socii
Ross, S. (2024, November). Information security matters: NIST CSF 2.0 and the cybersecurity hierarchy. ISACA Journal, 6. isaca.org/resources/isaca-journal/issues/2025/volume-1/nist-csf-20-and-the-cybersecurity-hierarchy
Whitman, M. E., & Mattord, H. J. (2021). Principles of information security (7th ed.). Cengage Learning.
World Economic Forum. (2025, January). Artificial intelligence and cybersecurity: Balancing risks and rewards [White paper]. World Economic Forum & University of Oxford Global Cyber Security Capacity Centre. weforum.org/stories/2025/01/a-leaders-guide-to-managing-cyber-risks-from-ai-adoption
FAQ
What is NIST CSF 2.0?
NIST Cybersecurity Framework 2.0 (NIST CSF 2.0) is a voluntary, risk-based framework published by the National Institute of Standards and Technology in February 2024. It organizes cybersecurity risk management across six core functions — Govern, Identify, Protect, Detect, Respond, and Recover — and is designed to scale from small businesses to large enterprises. It is widely recognized as a de facto international standard for cybersecurity program management (Ross, 2024).
Is NIST CSF 2.0 mandatory for SMBs?
NIST CSF 2.0 is technically voluntary, but it has become a de facto requirement in several contexts. Federal contractors, organizations pursuing cyber insurance, and vendors selling to enterprise buyers are increasingly expected to demonstrate CSF alignment. Regulators in financial services, healthcare, and critical infrastructure sectors reference CSF in sector-specific mandates.
What is the difference between NIST CSF 2.0 and CSF 1.1?
NIST CSF 2.0 adds a sixth core function — Govern — to the original five. The Govern function establishes cybersecurity governance, risk appetite, policy, and leadership accountability as a foundational layer underlying all other functions. CSF 2.0 also expands the framework's scope beyond critical infrastructure to all sectors and organization sizes, adds enhanced supply chain risk guidance, and explicitly addresses AI risk management (NIST, 2024a; Dempsey et al., 2024).
How does NIST CSF 2.0 help SMBs achieve SOC 2?
NIST CSF 2.0's six functions map directly to SOC 2's Common Criteria series. Building a documented CSF program — with a current profile, target profile, gap-closure roadmap, and continuous evidence collection — simultaneously constructs the control infrastructure required for a SOC 2 Type I engagement. The overlap is greatest in risk assessment (CC3), logical access (CC6), system monitoring (CC7), and vendor management (CC9) (IS Partners LLC, 2025).
Why does AI governance matter for NIST CSF 2.0 compliance?
AI tools — both sanctioned and unsanctioned (shadow AI) — expand the attack surface that all six CSF functions must account for. NIST's December 2025 Cyber AI Profile explicitly supplements CSF 2.0 with AI-specific risk guidance (NIST, 2025a). AI systems must be inventoried under Identify, governed under Govern, controlled under Protect, monitored under Detect, and included in incident response plans under Respond and Recover.
What is shadow AI and why is it a NIST CSF concern?
Shadow AI refers to AI-powered tools used by employees without IT or compliance approval — including chatbots, code assistants, and large language models. ISACA (2025a) notes that compared to authorized AI systems, shadow AI creates governance silos dangerous to enterprise risk management. IBM's 2025 Cost of a Data Breach Report found that shadow AI-related incidents accounted for 20% of global data breaches and were more expensive to resolve than other breach types (AICPA, 2025).
How does RAIC support NIST CSF 2.0 compliance for SMBs?
RAIC delivers a guided NIST CSF 2.0 assessment across all six functions and the complete subcategory catalog, producing a live gap heatmap scored by current and target tiers. Every gap converts into a tracked POA&M item with attached evidence. Cross-framework crosswalks map CSF subcategories to ISO 42001, NIST AI RMF, EU AI Act, and SOC 2. AI risk — including shadow AI — rolls up into the same posture report. Start a free trial at [app.rhindoncyber.com/trial-signup](https://app.rhindoncyber.com/trial-signup).
How long does it take an SMB to implement NIST CSF 2.0?
A current-profile assessment can be completed in hours using a guided platform like RAIC. Moving from assessment to a documented target profile and gap-closure roadmap typically takes one to two weeks for an SMB with limited security staff. Most SMBs target Tier 2 or Tier 3 maturity across most functions within 12–18 months, with foundational controls — MFA, EDR, privileged access hardening, backup testing — implemented within the first 90 days (NIST, 2024b).
Bring AI governance into one platform
Start a free trial of RAIC and operationalize the practices in this article.
Start trial