
ADD AI GOVERNANCE.
GET YOUR WEEK BACK.
RAIC gives IT and security teams a complete AI governance program out of the box — shadow AI discovery, automated evidence collection, and framework-mapped controls. Stop building it from scratch. Start operating it on day one.
AI governance is the new unfunded mandate.
It landed on the security team without a budget, without a headcount, and without an end date. The only way out is automation.
AI governance landed on your plate, not your roadmap
Leadership wants policy, evidence, and an attestation by Friday — on top of the patch backlog, the SIEM tune, and the audit you're already running.
Shadow AI is the new shadow IT
Half the company is pasting customer data into chatbots you've never approved. You can't block what you can't see, and you can't govern what you can't inventory.
Evidence collection is a part-time job
Every framework asks for the same controls in a different shape. Screenshots, spreadsheets, and quarterly fire drills — repeated for every auditor.
One AI incident away from a bad week
No playbook, no owner, no logged decision trail. The first model misfire becomes the post-mortem you're presenting to the board.
The hours back. Without the headcount.
Every capability in RAIC is designed to delete a task your team is doing today by hand.
Stand up a program in days, not quarters
Pre-built registers, policies, and control libraries mapped to ISO 42001, NIST AI RMF, and the EU AI Act. Activate a tenant, import your stack, and you're already 80% of the way there.
Shadow AI discovery on autopilot
A lightweight browser extension and Microsoft Graph integration detect supported AI services and model activity across the org, matched against RAIC's curated catalog — categorized, risk-scored, and ready to triage in one screen.
Aslan AI writes; agents keep watch
Aslan drafts risk assessments, gap analyses, incident playbooks, and control narratives from your live registers. Automation Agents run on a schedule between drafts — triaging Shadow AI finds, flagging stale evidence, and catching drift. Every agent action arrives as a proposal your team approves.
Evidence collects itself
Approvals, attestations, and control updates flow straight into the audit-ready evidence trail. The next assessment opens to a folder that's already populated.
One control library, every framework
Map a control once, satisfy ISO 42001, NIST AI RMF, EU AI Act, and SEC / FINRA AI in parallel. No more rebuilding the program for every auditor.
Plugs into the stack you already run
SSO, Microsoft 365, ticketing, and SIEM — RAIC connects in instead of asking your team to live in another portal. Governance happens where work already does.
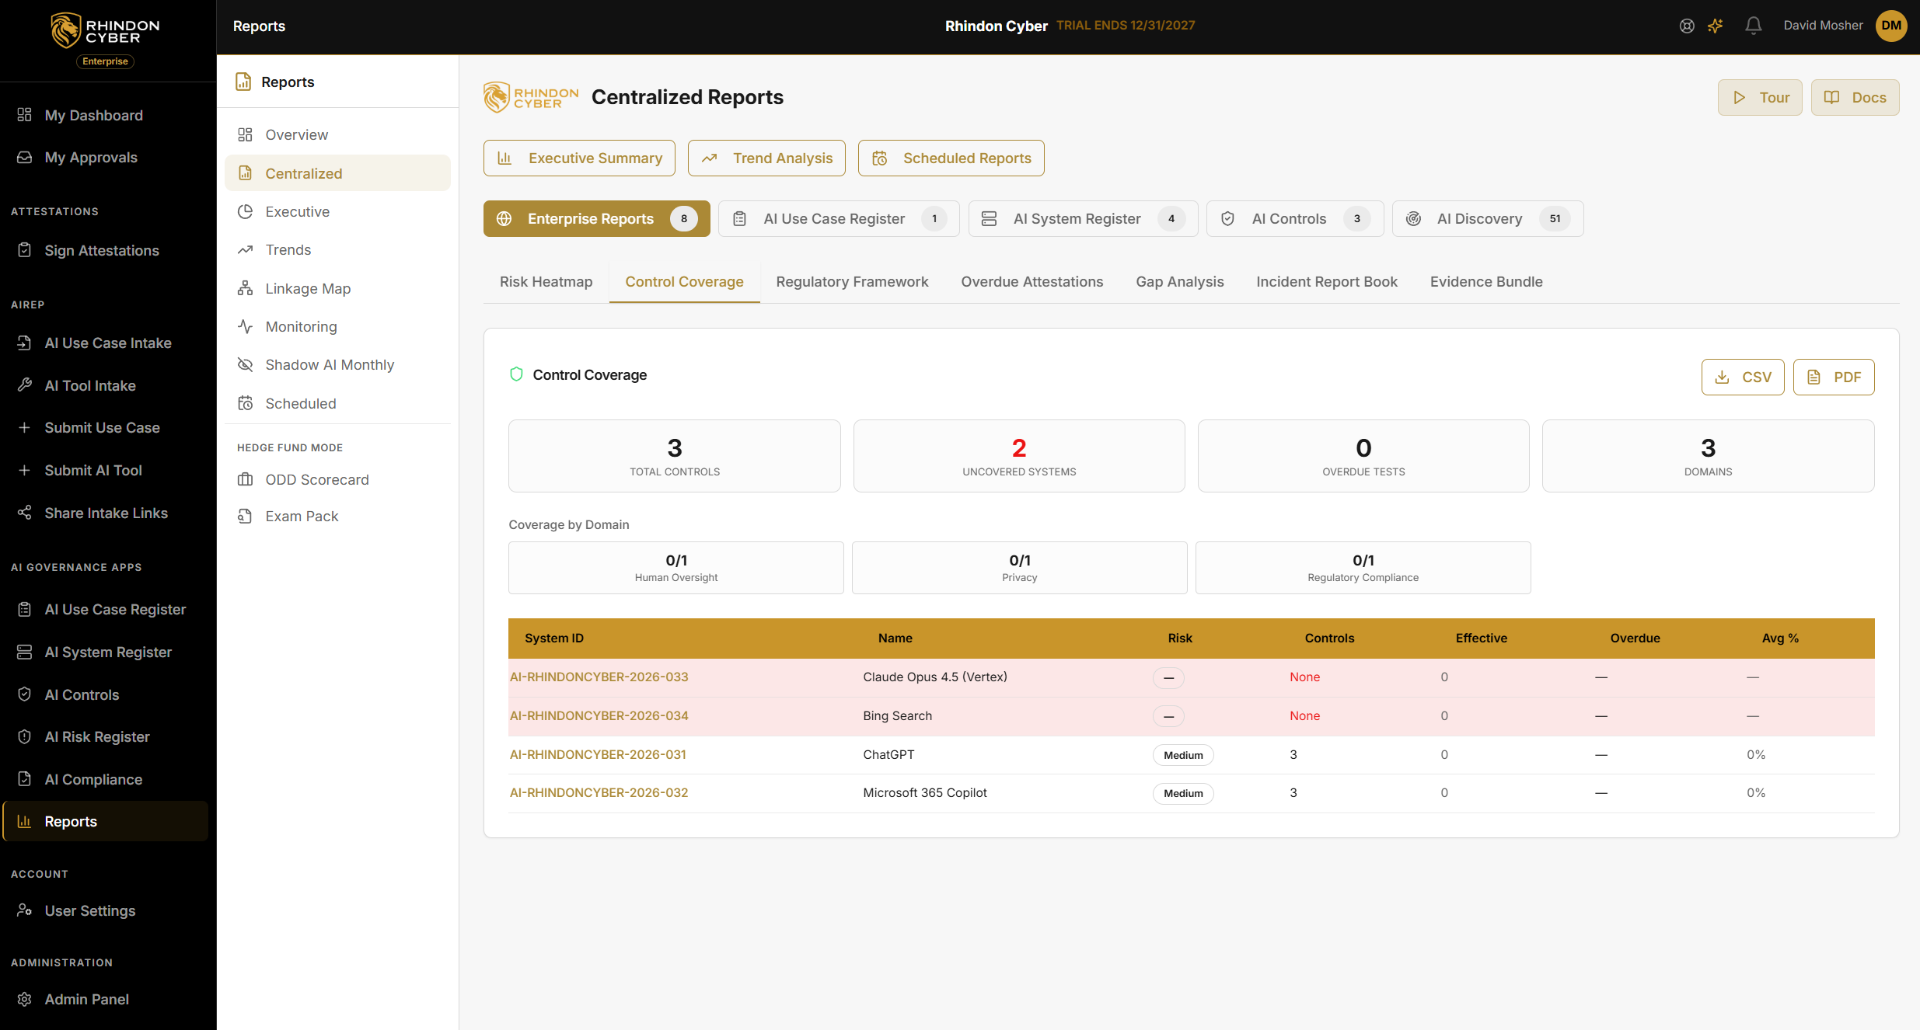
Centralized Control Coverage — every AI system, every control, every gap in one place.
Everything your team needs. One pane of glass.
Live registers, control status, attestations, and incident playbooks — surfaced where the security team already works.
AI footprint in one view
Sanctioned models, shadow tools, owners, business units — one register, always current.
Control posture, live
Which controls are active, which are slipping, and which need attention before the next audit window.
Attestation status without the chase
Who signed, who's overdue, and what changed — without a single follow-up email from you.
Incident playbooks, ready to run
Pre-built AI incident response with severity tiers, decision logs, and notification rules baked in.
Days to deploy. Not a six-month project.
Activate the tenant
SSO, role mappings, and the AI control library spin up in minutes. No services engagement required.
Discover the AI footprint
Deploy the discovery extension and connect Microsoft Graph. Sanctioned and shadow AI populate the register automatically.
Operate, don't author
Approve, attest, and triage from the inbox. Aslan AI drafts; your team reviews. Evidence trails itself.
The work that used to eat your week.
- Cut AI program setup from quarters to days
- Replace screenshot evidence with a live, audit-ready trail
- Find and triage shadow AI before the next pen test does
- Map one control to every framework instead of one program per auditor
- Hand the board a posture answer without a week of prep
- Free the security team to do security — not spreadsheet upkeep
AI adoption is not waiting for your roadmap.
Every week without a program is more shadow AI, more uncatalogued risk, and more evidence to reconstruct later. Teams that automate governance now ship policy in days. Teams that don't spend the next two quarters catching up.
From the Resources library
The Shadow AI and risk-management playbooks our security customers use.