
ENTERPRISE-GRADE AI GOVERNANCE.
BUILT FOR LEAN TEAMS.
RAIC gives resource-constrained organizations a complete AI governance program — policy, shadow AI discovery, audit-ready evidence, and framework-mapped controls — without an enterprise budget or a dedicated GRC team. Ship it this week.
AI governance was built for the Fortune 500. You are not the Fortune 500.
The regulators, the auditors, and your enterprise customers expect the same answers — without giving you the same budget to produce them.
Enterprise GRC tools are priced for enterprises
Six-figure platforms, six-month implementations, and a dedicated team to run them. None of that fits a 50- to 500-person company.
No GRC hire on the horizon
AI governance landed on the same person who runs IT, security, vendor management, and the SOC 2 renewal. There is no spare headcount coming.
AI tools showed up before policy did
Marketing is using one chatbot, sales another, engineering a third. None of it was approved. All of it touches customer data.
Customer questionnaires now ask AI questions
Enterprise prospects want a written AI policy, a vendor list, and an attestation. Losing the deal because you can't answer is worse than the cost of governing.
A full program. Right-sized for your team.
Every capability is tuned for organizations that need to operate the program with the people they already have.
A complete program out of the box
Pre-built AI policy, control library, registers, and attestations — calibrated for SMB scope. Activate today, hand it to your auditor next week.
Shadow AI discovery without the agent army
A lightweight browser extension and Microsoft 365 integration detect supported AI services and model activity, matched against RAIC's curated catalog. Get the picture in hours, not a quarterly survey.
Aslan AI is your governance analyst
Risk assessments, gap analyses, vendor reviews, and customer-questionnaire answers — drafted from your live registers in minutes. One person reviews; nobody starts from blank.
One control library, every framework
ISO 42001, NIST AI RMF, the EU AI Act, and the AI sections of SOC 2 — all satisfied from one set of controls. No parallel programs to maintain.
Evidence collects itself
Approvals, attestations, and policy acknowledgements flow into an audit-ready trail automatically. The next assessment opens to a folder that's already populated.
Priced for the team you actually have
SMB-tier pricing that costs less than the salary you would need to add to do this manually — and ships value the same week.
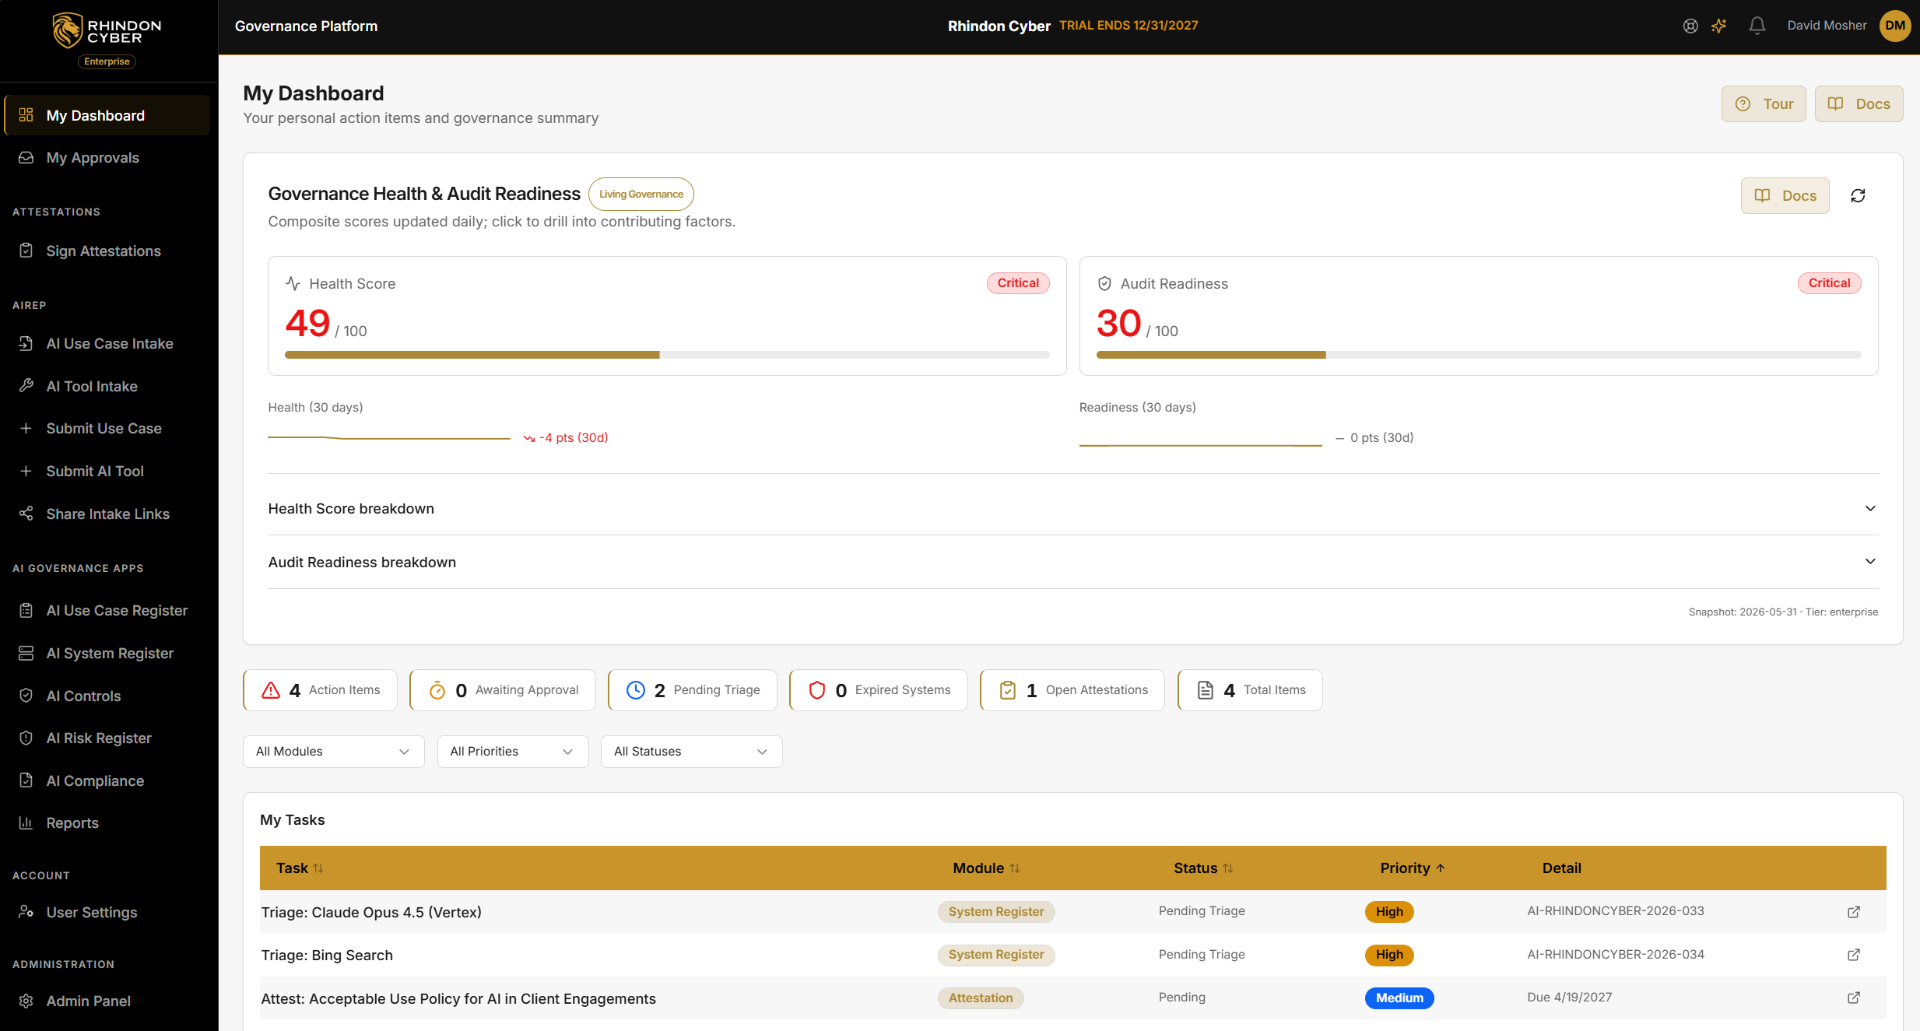
Your governance dashboard — health, readiness, and the next action in one place.
The answers you need. Without the overhead you don't.
Policy and posture in one place
Live AI policy, control status, and the evidence behind every claim — ready for customers, auditors, and your board.
AI inventory, always current
Sanctioned tools, shadow tools, owners, and risk tier — one register you can show to a prospect in 30 seconds.
Attestations on autopilot
Annual policy acknowledgements, vendor reviews, and use-case approvals run themselves. You approve exceptions.
Incident playbooks ready on day one
Pre-built AI incident response — severity tiers, decision logs, and notification rules — so the first event is not the first plan.
A week to stand up. A day to operate.
Activate in a day
SSO, role mappings, and the AI control library spin up the same afternoon. No services contract required.
See your AI footprint
Deploy the discovery extension and connect Microsoft 365. Your sanctioned and shadow AI inventory populates automatically.
Answer the AI question with confidence
Send the policy, share the posture, and answer the customer questionnaire in an hour — not a week.
The work that used to block deals and burn weekends.
- Answer customer security questionnaires without scrambling
- Ship a written AI policy in days, not next quarter
- Replace shadow AI with sanctioned tools and an inventory
- Pass SOC 2, ISO, and customer audits on the same evidence
- Govern AI without hiring a GRC analyst you can't afford
- Free the IT generalist to do IT, not spreadsheet upkeep
Smaller is not an excuse anymore.
Enterprise buyers, insurers, and regulators are pushing AI requirements down to vendors of every size. The SMBs that show up with policy, posture, and evidence keep the contracts. The ones that don't get screened out — quietly.
From the Resources library
The deep-dive playbooks behind this page.